Category: news
-
Bludgeon The Weak Premiere New Single & Music Video “Loss of a Figure” From 2026 EP “Execution”
Austin, Texas-based deathcore outfit Bludgeon The Weak premiere a new single and music video by the name of "Loss of a Figure". The track is taken from their current EP "Execution", out in stores now. Check out "Loss of a Figure" streaming via YouTube and Spotify for you now below. Read More/Discuss on Metal Underground.com -
Ice Nine Kills Join Forces With Tony Hawk & ‘Dead By Daylight’ For The Premiere Of Their “Play Dead” Music Video
Gold-certified metalcore outfit Ice Nine Kills have begun rolling out their new single, “Play Dead”, a horror-themed collaboration with the popular asymmetrical multiplayer game Dead By Daylight. The partnership adds another chapter to the band's long-running fascination with horror culture and media. Dead By Daylight itself has a history of… Read More/Discuss on Metal Underground.com -
BAEST Premiere “Stormbringer (Togskinner)” Video – Expand European & UK Tour Plans
Danish death metal force BAEST have released a new music video for “Stormbringer (Togskinner)”, an alternate version of the track “Stormbringer” from their latest album, “Colossal”. The railway maintenance-themed clip was directed by Martin Lundgaard and offers a fresh visual and musical interpretation of the song. By reimagining the origina… Read More/Discuss on Metal Underground.com -
“We got mad at a promoter and threw donuts at the wall backstage. Then we cleaned it up, because we felt guilty.” The unlikely triumph of rock’n’roll’s greatest nerds, the B-52s
How new-wave eccentrics The B-52s spun lobsters, aliens and Yoko Ono into floor-shaking hits and became massive -
Album Review: Lost in Kyiv – We’re All Going to Be Fine
Album Review: Lost in Kyiv – We’re All Going to Be Fine
The summer of 2026 is looking to be a special year for Lost In Kiev…oh, sorry, Lost In Kyiv! The French post-rockers now operate under the new name. With festival slots at Arctangent and Pelagic festivals this summer, what other doors will be opened with the name change? With a new full length record “We’re All Going To Be Fine” about to drop, can this be the catalyst to get more heads turning in the world of post-rock and the platform for increased festival appearances? Let’s find out…
No fancy introductions, straight into the crunching grooves; distorted and with plenty of attitude, much like a Pearl Jam or 90s grunge acts. There’s deceptive sense of complexity within the layers and layers of textures, much like a Cult Of Luna composition. Though from these murky depths, there are occasional melodic opulent burst to provide contrast to the mix, with the light shining brilliantly. The pace and dynamics shift constantly in a way that feel organic and well calculated rather than taking the scatter gun approach, hinting at a carefully considered compositional approach.

Then things take a turn during ‘Becoming’. An instrumental band at the core, Lost In Kyiv enlist the vocals of Rebecca from i HAXA, one of the new breed on Pelagic’s mighty deep roster. The music becomes much more stripped back and minimalistic in the early stages of the song, with just the drums, bass, and gentle guitar arpeggios making way for her ethereal and soothing voice to take centre stage! That doesn’t stop the band from piling on the pressure with crushing walls of atmospheric during the chorus though! The impact of such chorus is truly felt when held in comparison to the more soothing versus and ambient segments of this. Just one problem though; as an instrumental band, how will they replicate this in the live arena, assuming Rebecca isn’t available to tour?
Lost In Kyiv have always flirted with the addition of electronic music, with evidence of this in the early stages of ‘Euphoria’. The song title feeling very fitting giving the song’s bruising crescendo and highlight of this 9 minute journey, with the guitars being the focal appoint of this cinematic and atmospheric arc. ‘Liminality’ is another that demonstrates that Lost In Kyiv can successfully apply the tried and tested formula of calmer more ambient segments, to build tension and intrigue, that progress towards huge cathartic and uplifting bursts!
Overall, “We’re All Going To Be Fine” represents evolution and progression for the band, and whilst the album isn’t likely to provide a serious challenge to the crown of post-rock kings just yet, it’s a solid effort in it’s own right.
For all the latest news, reviews, interviews across the heavy metal spectrum follow THE RAZORS’S EDGE on facebook, twitter and instagram.
The post Album Review: Lost in Kyiv – We’re All Going to Be Fine appeared first on The Razor's Edge.
-
What You Should Never Share Online To Protect Your Privacy?
Treat your personal data as a high-value asset. In an era where automated data harvesting is the norm, information exposure acts as a roadmap for threat actors.
To maintain robust operational security (OPSEC) in 2026, you must strictly control any telemetry or identifiers that could facilitate synthetic identity creation, locate your physical person, or enable unauthorized account access.
This includes PII such as Social Security numbers, biometric identification, full birth dates, and residential addresses, as well as operational data like travel itineraries, financial credentials, and real-time location tracking.
The threat landscape has evolved beyond simple spam. FTC data for 2025 indicates that approximately 30% of reported financial fraud originated on social media platforms, with losses totaling $2.1 billion.
Furthermore, the FBI cybercrime report estimated the cost of cyber-enabled crimes at nearly $21 billion, as adversaries increasingly deploy sophisticated voice clones, deepfake media, and fraudulent documentation to bypass traditional verification.
The Basic Rule: Never Share Data That Identifies, Locates, Or Verifies You
Small details often become the missing piece in a larger identity puzzle|Shutterstock Proactive defense begins with a rigorous evaluation of every data point: could this information be leveraged by a threat actor to impersonate you, establish a physical location, or compromise a secure perimeter?
Data Category Primary Vulnerability Risk Mitigation Full birth date Facilitates account recovery abuse Disclose birth month/day only Residential address Enables physical stalking and data enrichment Utilize P.O. box for logistics Mobile number Vulnerable to SIM swapping and social engineering Use VOIP or encrypted messaging aliases Government Credentials Core identifiers for synthetic identity creation Submit only through end-to-end encrypted portals Boarding passes/QR codes Leaks PNR and sensitive booking telemetry Redact all machine-readable codes entirely Child’s school or routine Creates safety and privacy risk Share vague, delayed updates Security hints Enables brute-force or credential guessing Use high-entropy, random salt values The FTC’s Consumer Sentinel Network aggregated 6.5 million consumer reports in 2024. It is critical to note that Sentinel data represents unverified consumer reporting, providing a significant cross-section of the visible threat landscape rather than an exhaustive audit of all national fraud activity.
Government IDs, Bank Data, And Official Documents
Maintaining zero-trust principles means never transmitting high-sensitivity documents, including Social Security numbers, passport scans, tax forms, student IDs, or medical records, via public social channels or unencrypted messaging platforms.
A digitized identification card provides threat actors with a template for identity duplication. Tax and financial documents contain dense clusters of PII (income, dependents, routing numbers) that can be leveraged for sophisticated phishing and account takeovers.
Use secure portals, company domains, written policies, and known phone numbers before uploading any document. Pressure is often the signal, not proof of urgency.
Passwords, One-Time Codes, And Security Answers
Authentication data should remain private, regardless of who asks for it|Shutterstock Strict confidentiality must be maintained for all passwords, passkey phrases, and authenticator tokens. NIST digital identity guidance explicitly mandates that subscribers are responsible for the protection of authentication secrets and prohibits their disclosure to third parties.
One-time passwords (OTPs) are frequent targets for social engineering. Adversaries frequently spoof trusted entities, banks, tech support, or corporate desks, to request OTPs. Under no circumstances should a legitimate support agent require your active authentication code.
Security-question answers also belong offline. Mother’s maiden name, first pet, first school, hometown, favorite teacher, and first car often appear in old posts, family comments, quizzes, or public records. Treat security answers like passwords: random, unique, and stored safely.
Birth Date, Phone Number, Address, And Location
Avoid the publication of full birth dates, mobile numbers, or specific location telemetry such as residence details and planned itineraries. CISA advises users to implement strict privacy settings, omit location-specific metadata, and disable active location tracking.
A quick check with VeePN can also show what your public IP address reveals about your connection, including location and ISP signals.
A full birth date can help match leaked data across old accounts, public records, breach dumps, and credit files. A phone number can act as a recovery key for banks, email, social media, delivery apps, and payment tools. Vacation posts and routine check-ins can also create predictable real-world patterns.
Regulatory protections do not eliminate risk. As of April 2026, 20 U.S. states had enacted comprehensive consumer privacy legislation, yet enforcement frameworks and data subject rights remain fragmented across jurisdictions.
Photos That Reveal More Than Planned
Photographic media often contains significant secondary data. Images can inadvertently capture workstation screens, financial receipts, hardware tokens, or reflections that provide actionable intel for an adversary.
Before posting, zoom in. Check corners, mirrors, windows, desk surfaces, fridge calendars, and background paperwork. Cover QR codes and barcodes completely, not with light scribbles. Cropping is safer than blurring when the hidden detail is sensitive.
Children’s Personal Information
A child’s digital footprint can begin long before they understand privacy risks|Shutterstock Do not disclose a minor’s full legal name, school affiliation, or medical history. Children are particularly vulnerable to long-term digital footprint risks and social engineering through overshared family routines.
Children inherit a digital record they did not choose. A back-to-school photo can reveal a school crest, teacher name, grade, bus route, and birthday clues. Use nicknames, private albums, small audience settings, and delayed posting.
What Can You Share Safely?
Effective OPSEC relies on de-identifying data, implementing temporal delays in posting, and utilizing the principle of least privilege for audience access.
Higher-Risk Post Safer Version Real-time location and duration telemetry Delayed, non-specific status updates Unsecured transmission of ID documentation Verified, out-of-band identity confirmation Visual identifiers of sensitive daily routines Anonymized media with redacted identifiers Financial documentation exposure Verbal mention only; image suppression Workstation/environment captures Sanitized environment with clear desk policy The goal is not silence. The goal is control over who gets enough information to act against you.
A 10-Minute Privacy Check
Run a fast audit every few months:
- Enforce strict audience isolation on all social profiles.
- Purge all PII (phone, DOB, residence) from public-facing metadata.
- Disable active geospatial tagging across all application suites.
- Perform regular OSINT audits of personal identifiers via private sessions.
- Replace security answers with high-entropy strings managed via a password vault.
- Mandate hardware-based or app-based multi-factor authentication (MFA).
- Scrub historical data for legacy exposure points and archived routines.
The Identity Theft Resource Center reports over 25,200 U.S. data compromises since 2005, exposing approximately 79 billion records.
The 2025 data breach report underscores how oversharing provides the necessary context for adversaries to weaponize leaked data through cross-referencing and enrichment.
What To Do If You Already Shared Too Much
Fast action can significantly reduce the consequences of data exposure|Shutterstock If sensitive information is already online, act quickly: delete the post, ask others to remove copies, change exposed passwords, revoke old app permissions, freeze or replace cards, and monitor account activity.
In the event of high-sensitivity data exposure (SSN, banking, or tax credentials), immediately execute a recovery plan. The FTC provides standardized identity protection steps to facilitate remediation through verified channels.
Implement credit freezes to mitigate the impact of identity compromise. CFPB guidance details how security freezes restrict access to credit reporting, preventing unauthorized account creation.
Summary of Defense Objectives
Mitigate the exposure of identifiers that facilitate identity theft, account compromise, or physical tracking. AI advancements and breach data markets have increased the utility of fragmented data.
A single identifier, a birth date, a badge photo, or a mobile number can serve as the pivot point for a targeted attack. Robust privacy now requires a strategy of high-friction data sharing: less detail, significant temporal delays, and strictly limited audience permissions.
-
“The area was being evacuated. The police knocked our door and the letting agency told us to leave. We decided to stick it out”: Marillion’s Pete Trewavas on the storms, earthquakes and blizzard that birthed the third Edison’s Children album
Assisted by a lunar astronaut’s son and a Hollywood special effects creator, 2019’s The Disturbance Fields defined the band’s mission to save this world, and others -
Album review: CARL CARLTON & MELANIE WIEGMANN – Miles Of Time
 Timezone [Release date 23.01.26] ‘Miles of Time’ is the second album by Americana style German duo of Carl Carlton and Melanie Wiegmann. Carlton is an experienced singer-songwriter, guitarist and producer (Robert Palmer, Herman Brood, Udo Lindenberg,The Songdogs, Manfred Mann, Eric … Continue reading
The post Album review: CARL CARLTON & MELANIE WIEGMANN – Miles Of Time appeared first on Get Ready to ROCK!.
-
THE DAMNED’s CAPTAIN SENSIBLE Reflects On 50 Years Of Punk Chaos
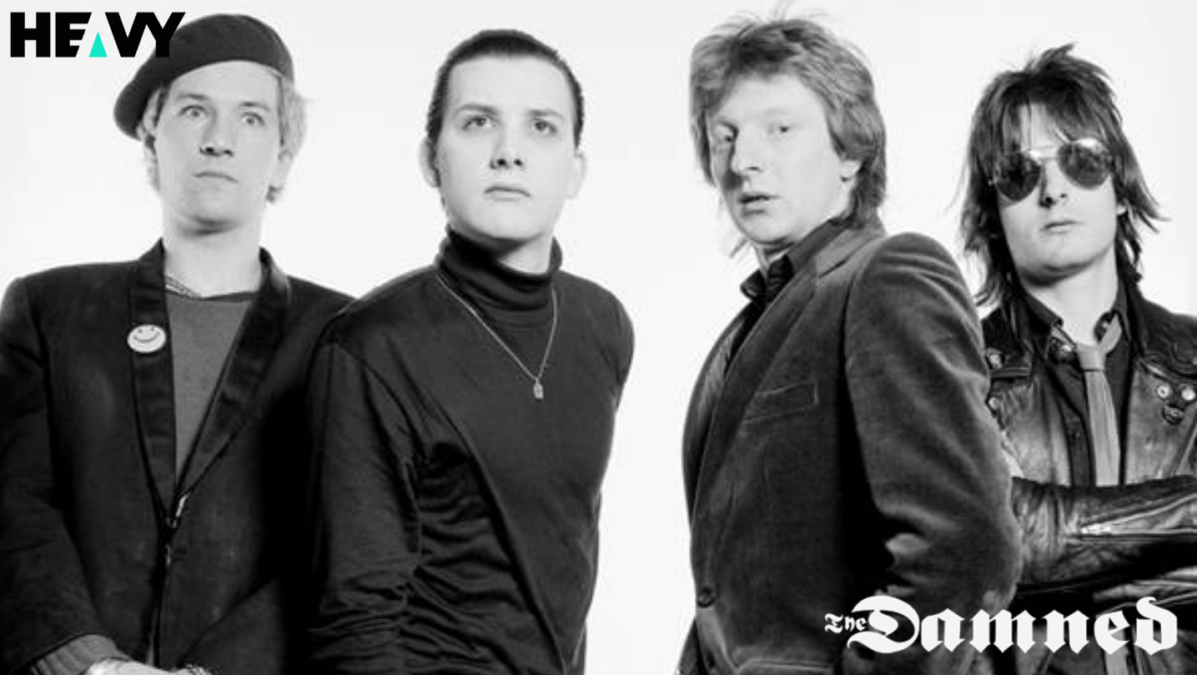 Interview by Angela Croudace Fifty years after helping ignite the UK punk movement, Captain Sensible still sounds pleasantly surprised that The Damned are standing strong. Speaking ahead of the band’s Australian 50th Anniversary Tour this September, the guitarist reflected on a career that has taken the group from playing tiny pubs to prestigious venues that […]
-
Not Beating Around The Bush With BRENT SMITH From SHINEDOWN
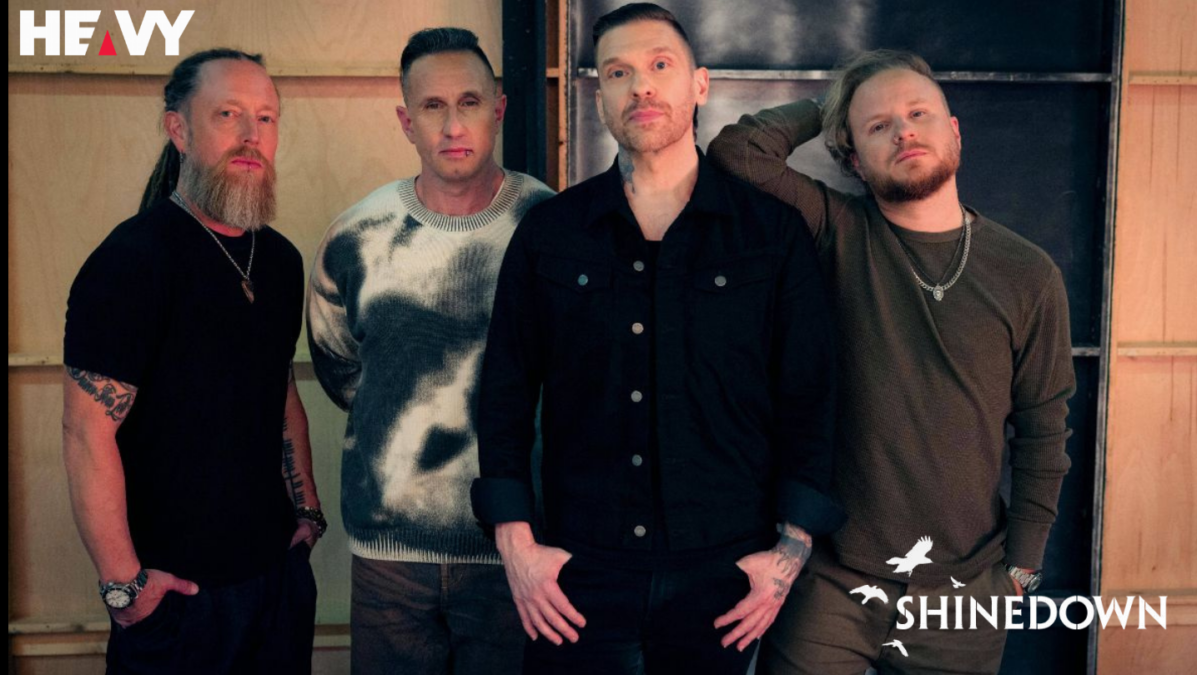 American rock titans Shinedown and British alternative legends Bush are uniting for a massive co-headline tour across Australia and New Zealand in September 2026. Promoted by Destroy All Lines, this blockbuster arena run bridges two distinct eras of heavy guitar music. The highly anticipated roadshow represents Shinedown’s monumental return down under for the first time […]